
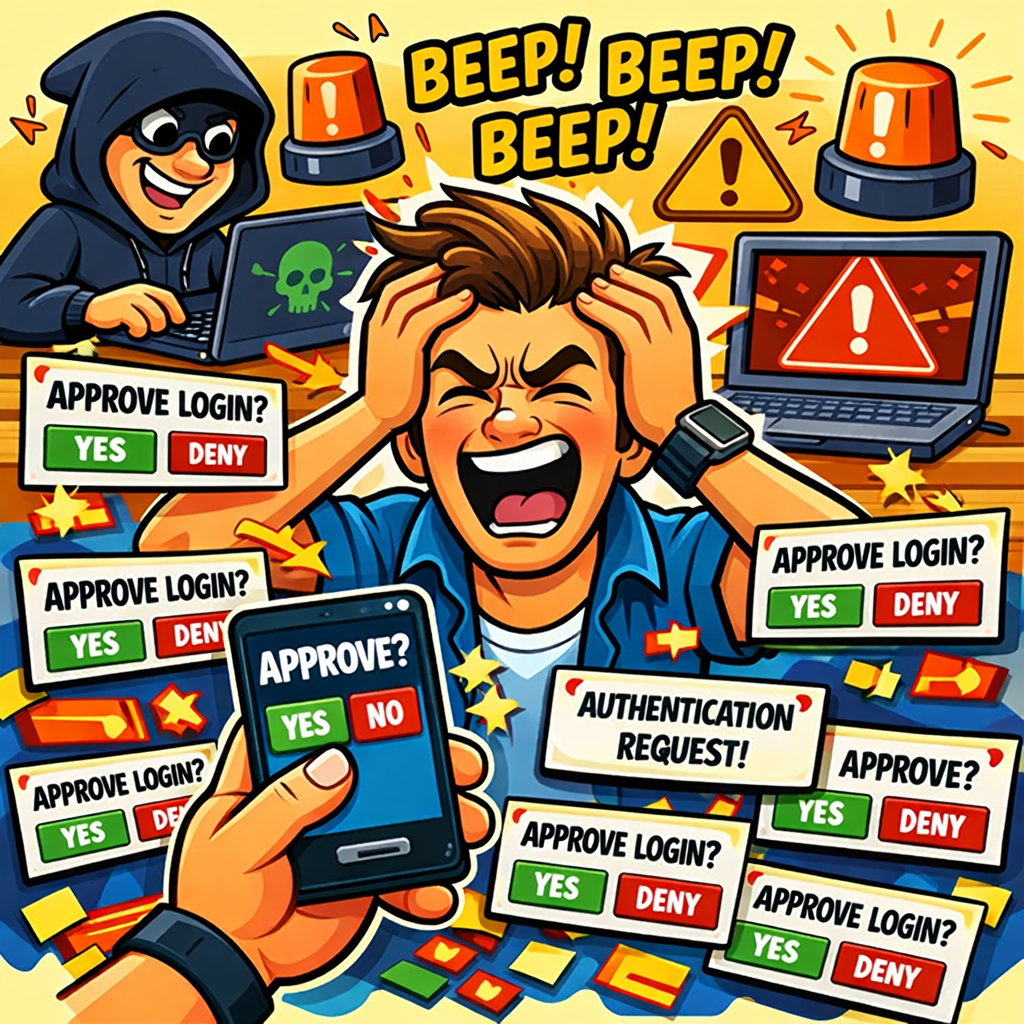
MFA Prompt Bombing: When Your Second Factor Becomes Your Worst Frenemy
If you’ve ever been jolted awake at 2:13 AM by your phone buzzing like it’s trying to escape the nightstand, congratulations. You may have experienced the modern cyber equivalent of water torture: MFA prompt bombing.
It’s the attack that proves hackers don’t always need elite skills or fancy tools. Sometimes all they need is persistence, a stolen password, and the confidence of a toddler who won’t stop pressing a doorbell.
Stop Feeding the Machines: How to Keep Your Chatbot From Using Your Data as Brain Food
If you’ve ever typed something mildly unhinged into a chatbot at 2 AM and thought, “Wow, I hope no engineer ever sees that,” congratulations, you’ve already discovered the number‑one reason to turn off model training.
Every major AI assistant wants to “improve the model for everyone,” which is corporate‑speak for “please donate your conversations so we can make the robot smarter.” And look, that’s not inherently evil. But it does mean your chats can be reviewed, analyzed, and used as training material.
OpenClaw’s Chaos 4 Pack: Why Your Favorite Crabby Assistant Is Back In The Hot Seat
If you thought OpenClaw was done causing trouble, think again. Our favorite crabby digital sidekick is back in the headlines with a fresh Chaos 4 Pack of vulnerabilities that let attackers steal data, boost privileges, and stick around longer than a glitter spill on carpet. And just like glitter, once it gets into your environment, it spreads everywhere you don’t want it.
When AI Starts Finding Zero‑Days for Hackers, It’s Time to Refill Your Coffee (And Your Security Budget)
Well, it finally happened.
Google just confirmed the first known case of a threat actor using AI to develop a real, live, in‑the‑wild zero‑day exploit. Not a proof‑of‑concept. Not a research demo. Not a “look what we can do in a lab with 47 GPUs and a grant from DARPA.”
A genuine, operational, malicious exploit — discovered, analyzed, and weaponized with the help of an AI system.
Welcome to the future. It’s loud, it’s messy, and it’s already trying to bypass your 2FA.
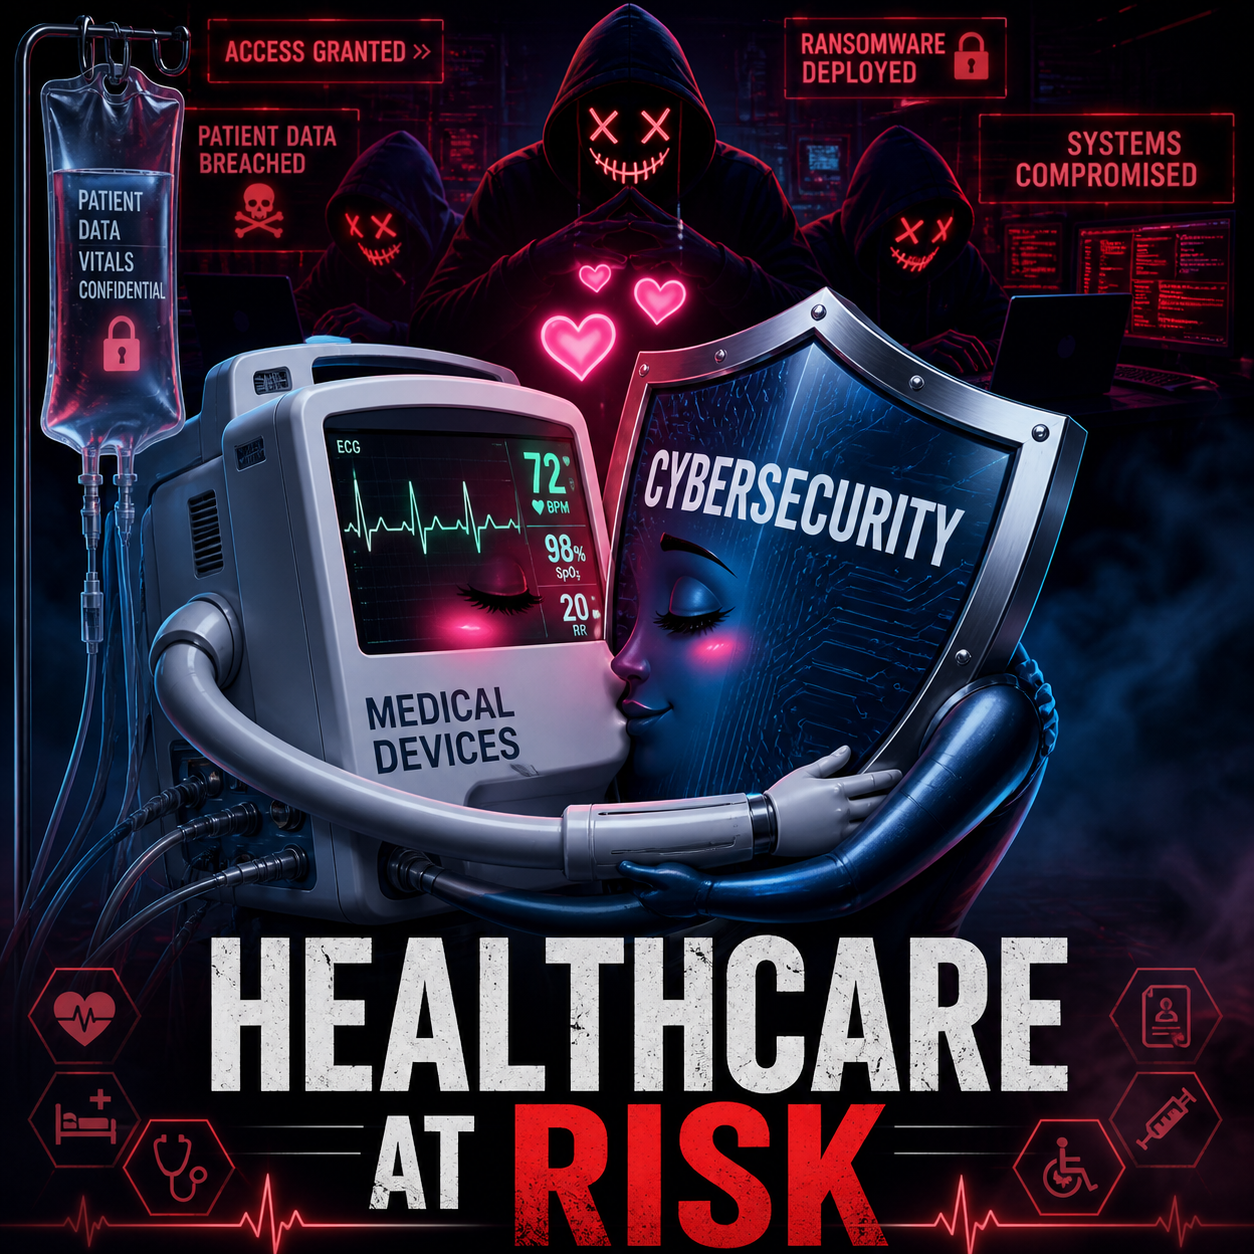
Cybersecurity And Medical Devices: A Love Story No One Asked For
Cybersecurity and medical devices go together like toothpaste and orange juice. Technically they can coexist, but nobody walks away feeling good about it. And yet here we are, living in a world where life‑saving equipment is increasingly connected, increasingly targeted, and increasingly running on operating systems that should have been retired back when flip phones were still cool.
The healthcare sector has always been a magnet for cyberattacks, but medical devices have become the new favorite playground for threat actors. Why? Because they’re connected, they’re critical, and they’re often secured with the digital equivalent of a sticky note that says “Do Not Touch.” Spoiler alert: attackers touch it anyway.